Phishing Incident Reports
When a suspicious email goes unreported, the security team learns about it late, or never. AwareX gives employees a familiar inbox route to raise the concern.
Explore the productsA threat noticed but not reported leaves the team in the dark.
A suspicious email left unreported keeps security teams in the dark. AwareX gives employees a familiar inbox route to raise the concern.
- 01 / WHAT ROUTINE TRAINING MISSES
The lesson stops at ‘do not click.’
An unclear reporting route can leave people ignoring a message or forwarding it around without reaching the right team.
- 02 / WHEN THE REQUEST FEELS REAL
The same request can keep reaching colleagues.
Delayed reporting can slow the security team’s awareness of a suspicious message that others may also receive.
- 03 / WHERE AWAREX CHANGES THE REHEARSAL
Give the pause a clear next action.
AwareX’s Phish Reporter Button provides an inbox reporting route. Confirm supported clients, triage, and feedback options in your demo.
Routine compliance training vs. AwareX
Compliance learning establishes a foundation. AwareX puts AI behind the action: it connects a suspicious message to the right reporting route and the feedback that follows.
| What matters | Routine compliance training | AwareX approach |
|---|---|---|
| Starting point | A scheduled course built around policies and general awareness. | AI studies your approved business context first, so the first test reflects how you work. |
| Workplace relevance | The same broad examples for every responsibility. | AI drafts role-specific versions for finance, HR, IT, and leadership; your team approves each. |
| What people practice | Recognizing terms and selecting answers in a lesson. | AI adapts the messages people meet and the guidance they receive. |
| Follow-through | Completion often becomes the finish line; reinforcement is rarely built in. | AI tracks how each message is handled and drafts the feedback that closes the loop. |
| What success means | Attendance, course completion, and assessment scores. | Concerns raised through the approved route, with AI spotting the pattern organization-wide. |
This compares a completion-focused training approach, not every training provider. AI output is reviewed by your team before release, and capabilities and scope are confirmed in your demo. Training does not guarantee attack prevention, compliance, or certification.
From recognizing a message to rehearsing a response
Can the employee report the suspicious email through the approved inbox process?
Rehearse the decisionExplain the missed cuePractice again
Phishing Incident Reports
Make reporting a suspicious email part of the everyday security routine.
How AwareX AI makes this more effective.
An AI agent reads the business context (roles, departments, current activity) so every test feels like it was written for that person.
AI drafts each scenario; your team reviews and approves it before anyone sees it.
Every response feeds the learning loop, so the next test and coaching match what each person actually needs.
AI proposes; people decide. Every scenario is reviewed and approved by your team before it reaches an employee.
From suspicious request to a safer response.
A marketing offsite, a campaign plan, and a board review, explored through this category’s approach.
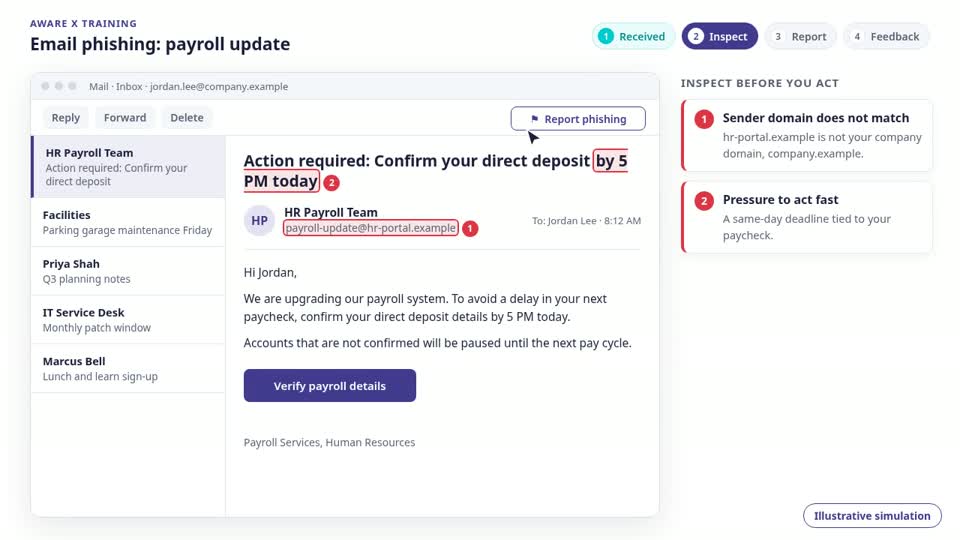
- A realistic message lands in the flow of work.
- Each cue is inspected one by one, from the sender to the deadline.
- The safe response is rehearsed: report it, verify it, or ask.
Verify new bank details first.
Illustrative screens, not live product screenshots. Messages, identities, and destinations are fictional; no links, payments, approvals, or uploads are active. Confirm capabilities in a demo.
One check today.
A safer routine every day.
Include reporting in every fire drill. Practice noticing the cue and raising the concern, so avoiding a click is not the end of the exercise.
Explore the fire-drill approachCaptured platform preview. Figures are example data, not measured customer results.
- 01
A drill, not a checkbox
A signed policy fades within weeks. A rehearsed pause, verify, and report habit holds when a real message lands.
- 02
Practice where decisions happen
Short, contextual exercises arrive in the flow of work, in the channels your teams actually use, instead of a once-a-year course.
- 03
Learn, never blame
A miss is data for the next exercise, not a mark against a person. Repeated practice is what moves the numbers.
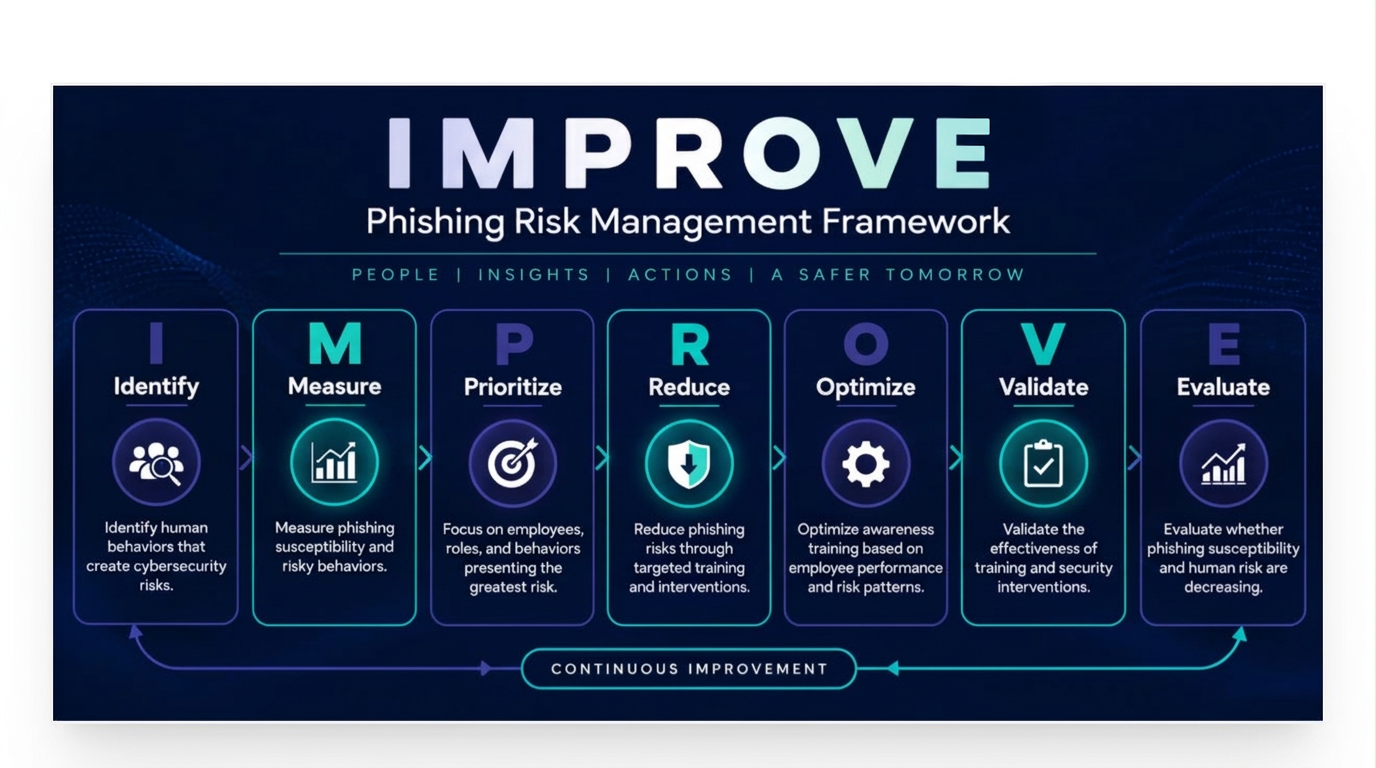
IMPROVE.
One continuous loop.
Identify, Measure, Prioritize, Reduce, Optimize, Validate, and Evaluate. AI connects business context, employee responses, and targeted learning to inform each next test.
AwareX is a human risk management platform.
One platform to assess, manage, and reduce the cyber risk that comes from human behavior, so the attacks it rehearses are the attacks that actually happen.
Phishing simulation
Authorized email simulations, AI-drafted from your business context, scoped by department.
Human risk assessment
Composite risk score from every send, click, credential, and report, trended by department.
Awareness & targeted training
Micro-modules with quiz and reminders, assigned to the people an assessment shows need them.
Analytics & reporting
Dashboards, funnels, department heatmaps, and board-ready PDF export.
PhishRadar
Lookalike-domain discovery and defensive registration: a control, not just a test.
Integration & governance
Microsoft Entra / AD sync, append-only audit trail, seat licensing, role-based admin.
AI you control
Default model, your own provider, or a fully local LLM; every AI decision logged.
SaaS or on-premises
Cloud or air-gapped license file. Your data stays where you need it.
Identify · Simulate · Measure · Improve in one governed, five-step pipeline.
Choose your next focus.
Clarity before
the next step.
What is phishing incident reporting?
Phishing incident reporting is the process employees use to alert the security team to suspicious messages or related interactions. A clear reporting path helps concerns reach the people responsible for review and response.
What does AwareX offer for reporting suspicious email?
AwareX presents the Phish Reporter Button as an inbox-based reporting option. Confirm deployment, email compatibility, routing, and handling scope in a demo before planning its use.
What information should an employee include in a phishing report?
Follow the approved process and describe what happened, including any clicks, submitted information, downloads, or access approvals. Preserve the original message where your process requires it, and avoid forwarding suspicious material widely.
Should employees report a suspicious email if they are unsure?
Yes, follow your organization’s guidance for reasonable concerns. Reporting asks the security team to review the message; employees do not need to prove that it is malicious before raising a concern.
What if an employee has already acted on a phishing request?
Report immediately through the approved incident channel and describe the action taken. Follow the security team’s recovery instructions. Prompt, accurate reporting is more useful than delaying because of embarrassment or uncertainty.
How does reporting support a security awareness program?
Reporting provides a practical next step after recognizing an unsafe request and can inform follow-up guidance. It complements training and technical controls; it does not by itself establish that every threat has been detected or contained.